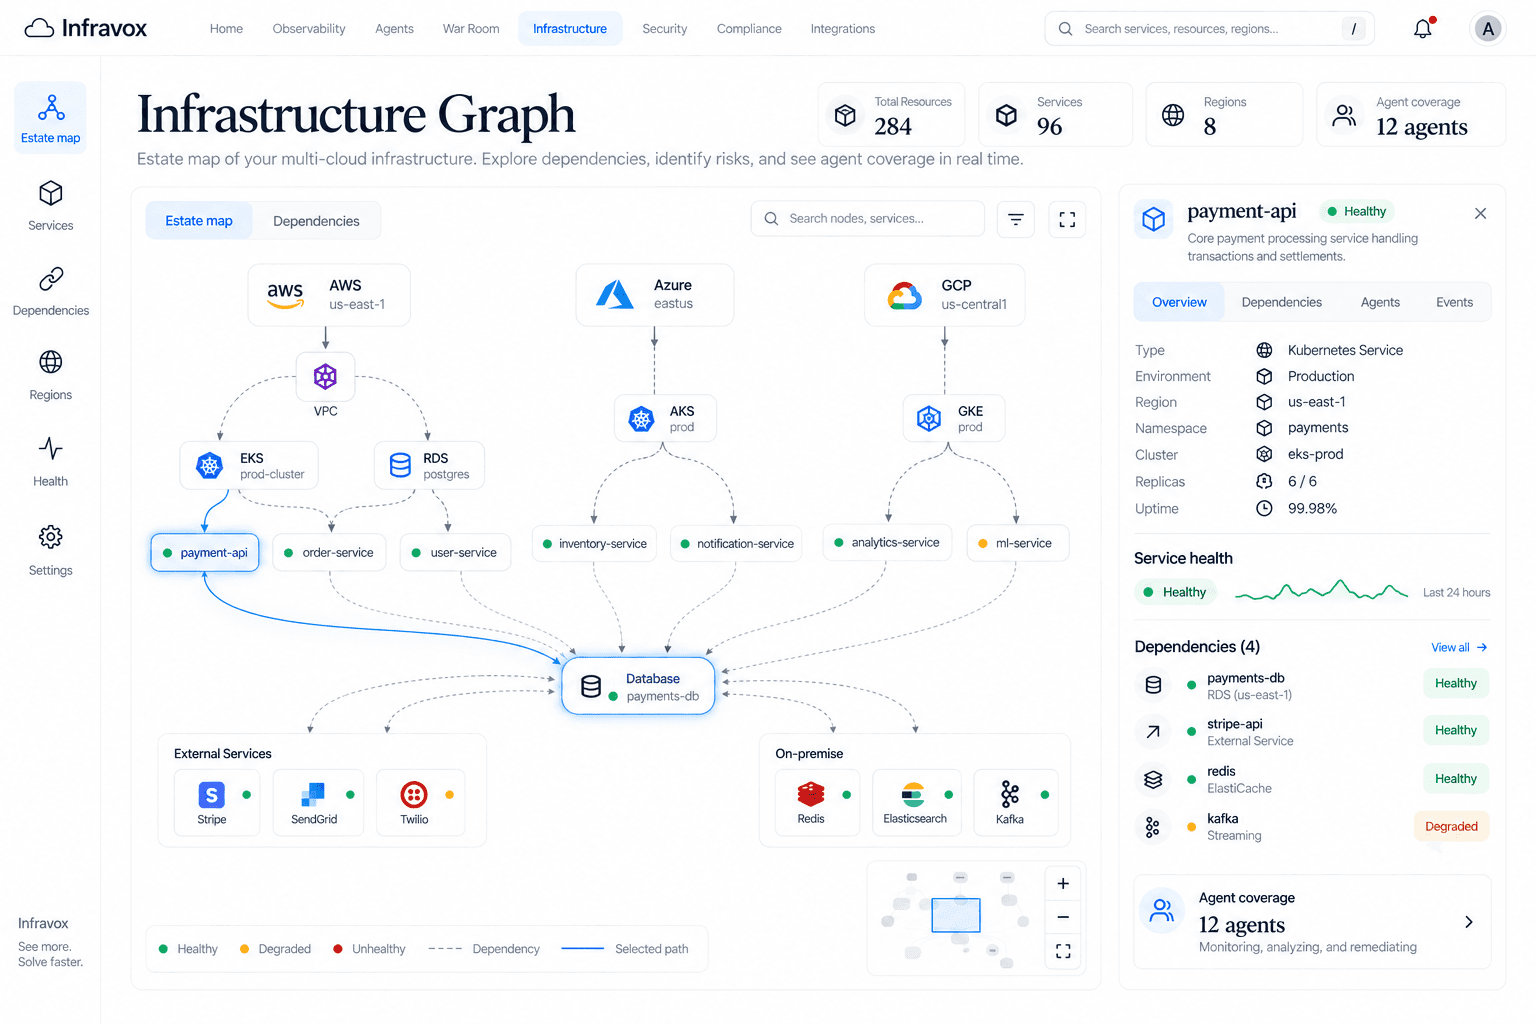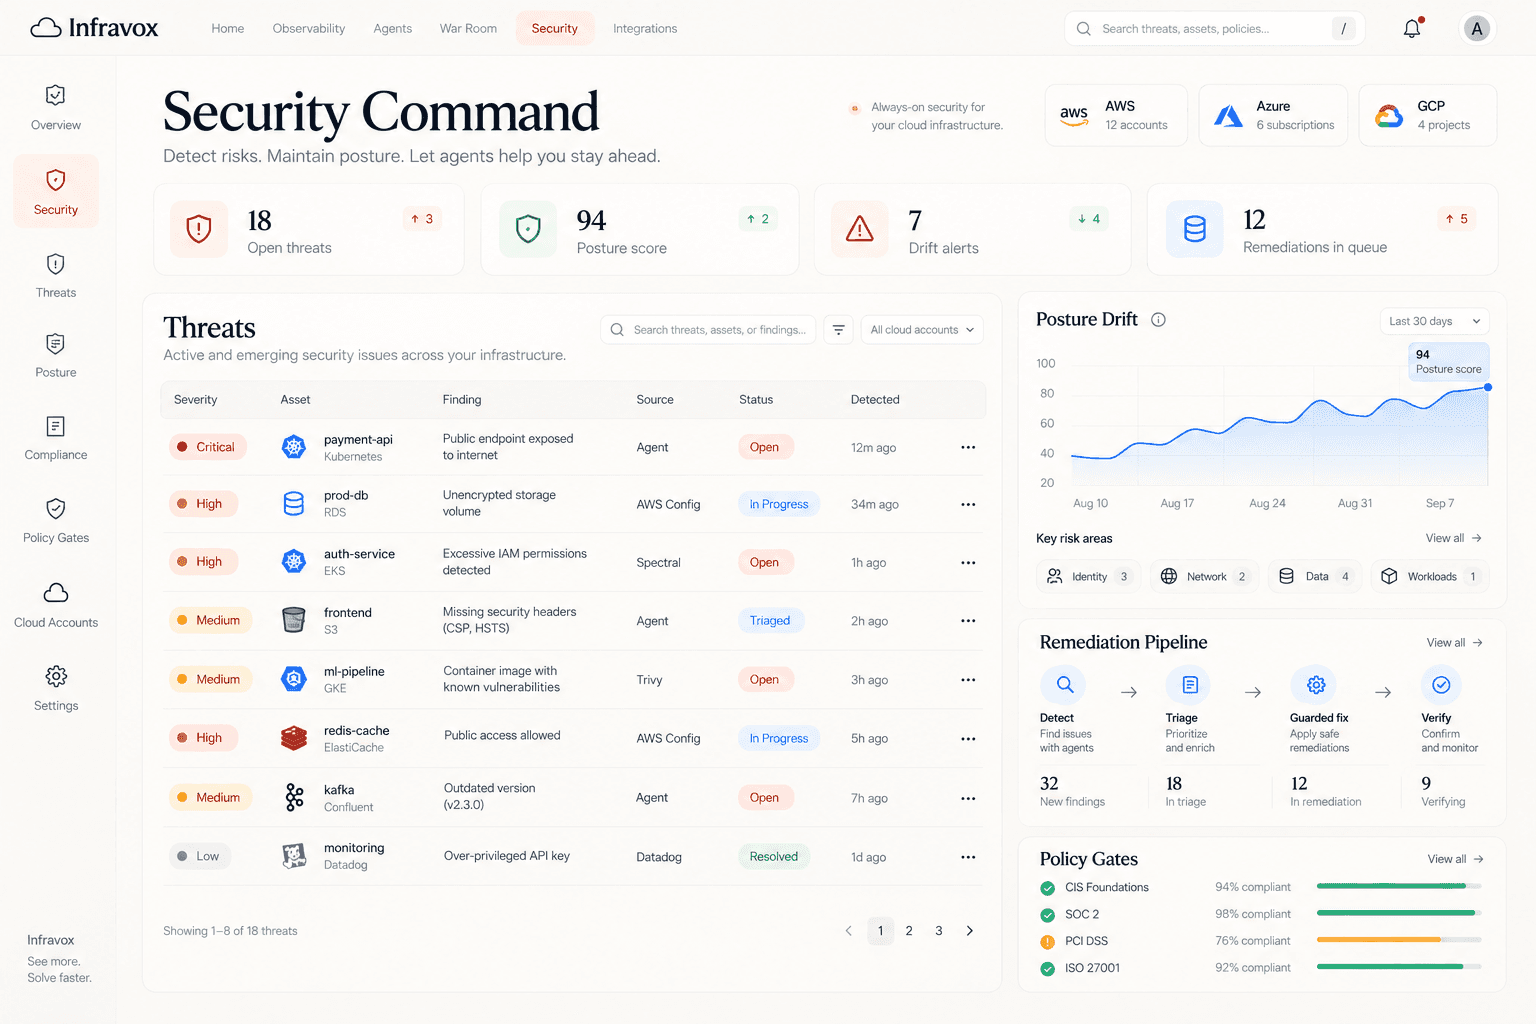
Posture that understands your graph
Continuous scanning across accounts and providers — findings ranked by blast radius, not raw volume.
- Multi-cloud account coverage
- Drift and exposure signals
- Evidence linked to resources
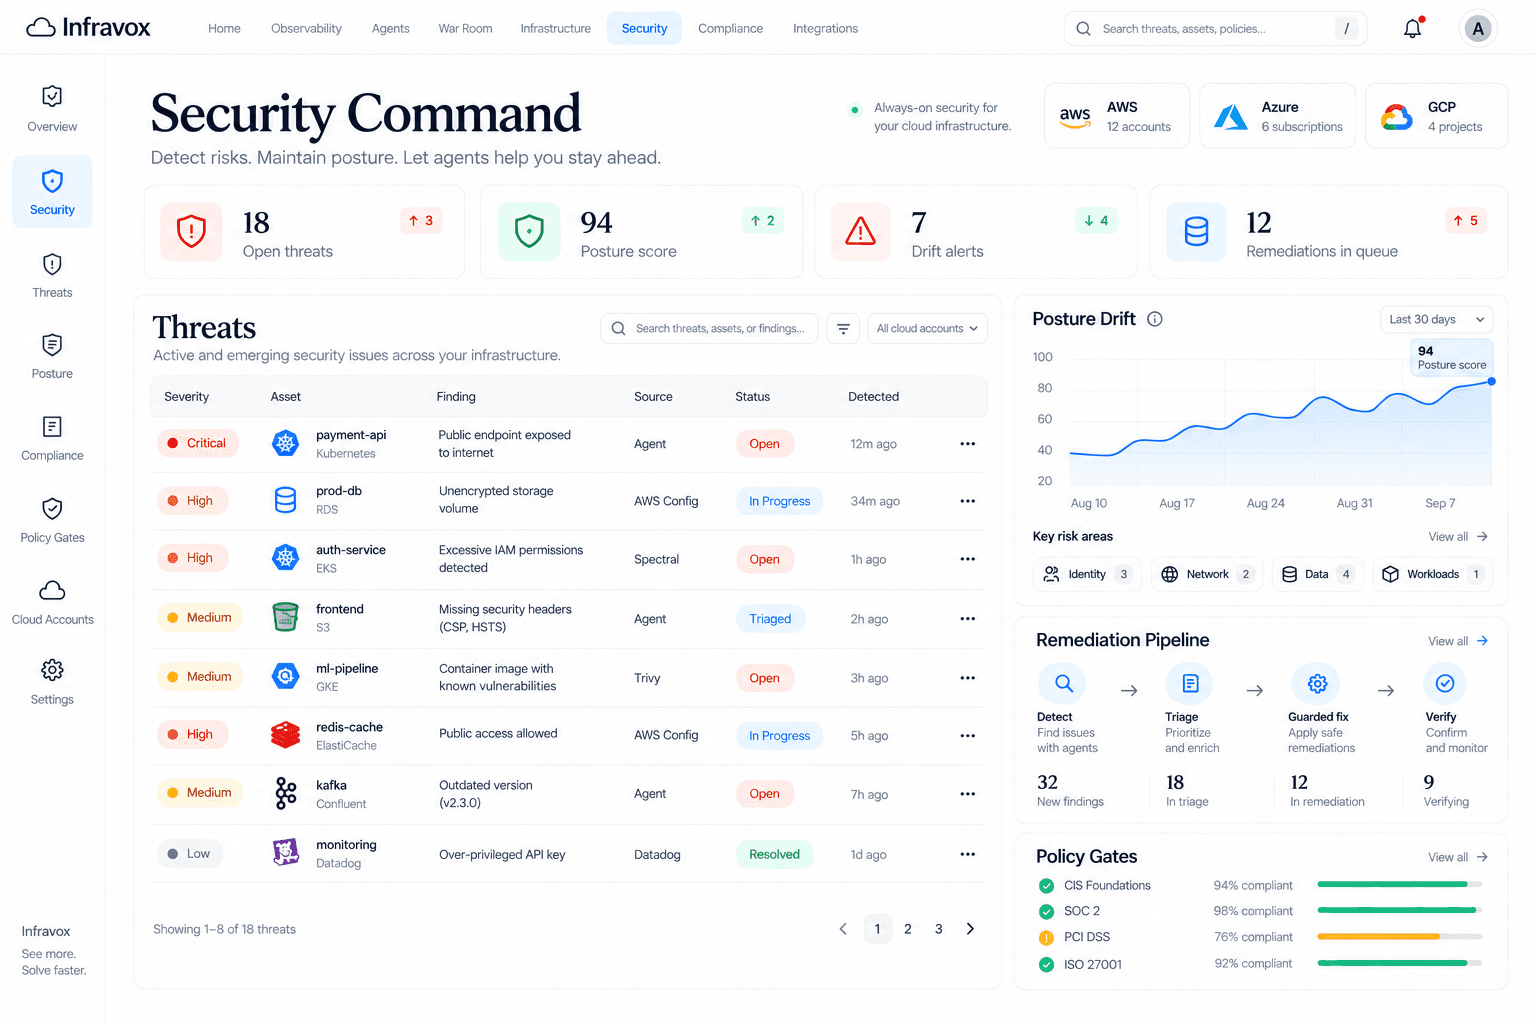
CSPM, CWPP, identity risk, secrets, and attack paths in one operating loop — continuous, agent-driven, and guarded by policy.

Mapped
Attack paths across identity, network, and workload edges
Closed
Misconfigurations before they become incidents
Reduced
Identity and privilege risk with least-privilege defaults
Everything in Cloud Security — represented as the control plane, not a icon grid.
Continuous control checks across every connected account.
VMs, containers, and serverless under one protection loop.
Entitlements, privilege score, and anomalous access.
Exposed credentials in code, configs, and pipelines.
Segmentation and exposure checks at every layer.
AI-driven log analysis with evidence you can act on.
Enterprise ready from day one. A category defining intelligence layer meticulously engineered for the complexity of Fortune scale cloud operations.
AWS, Azure, Google Cloud, Kubernetes, Terraform, Datadog & more