Trust & Security
Enterprise trust for an autonomous infrastructure future.
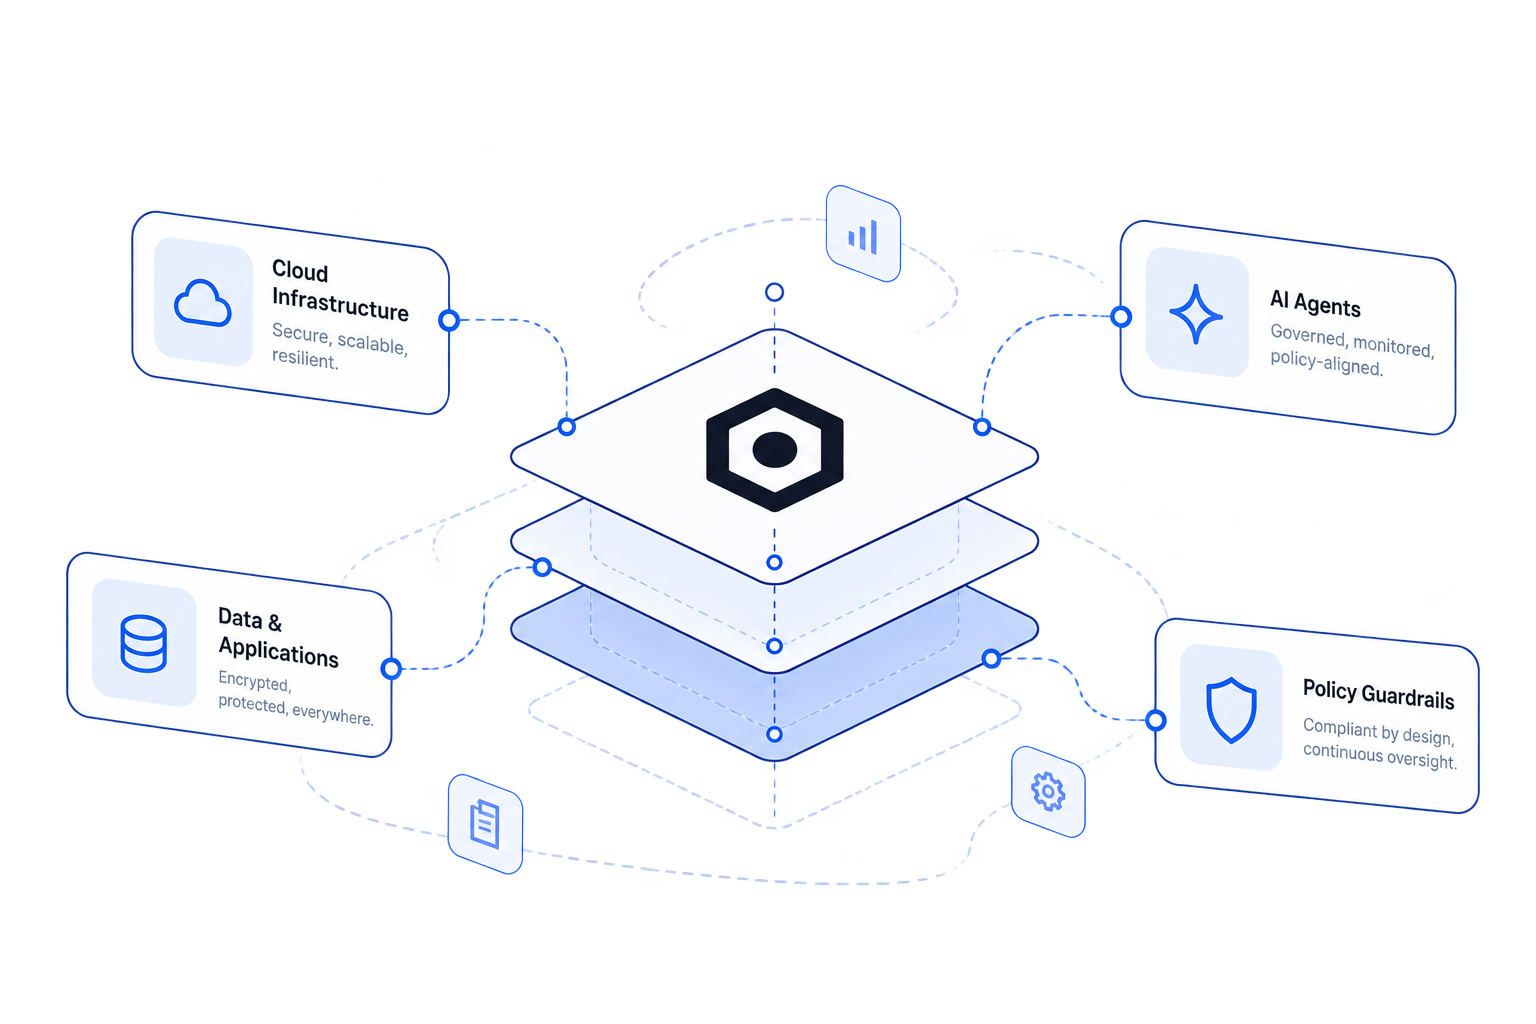
Security. Compliance. Transparency. Built into every layer of the Infravox OS.
- Zero-trust access with SSO, MFA, and RBAC
- Encryption in transit and at rest
- Honest compliance status — no invented pass rates
Security principles
Zero trust
Verify every identity, session, and action before access.
Data encrypted
TLS in transit and encryption at rest for tenant data.
Least privilege
SSO, MFA, SCIM, and role-based access by default.
Continuous monitoring
Audit trails, anomaly signals, and always-on posture checks.
Trust by design
TLS + AES
Data in transit & at rest
Tenant
Scoped isolation
RBAC
Least privilege access
Audit
Immutable activity logs
24/7
Security monitoring
Certifications
We're committed to ensuring security and compliance. We're GDPR-ready and advancing SOC 2 Type II and HIPAA programs — with honest status, not invented pass rates.
Layered protection
Security at every layer
Defense in depth across people, process, and platform — with policy guardrails on every autonomous action.
- Identity & Access
SSO, MFA, SCIM provisioning, and role-based access control.
- Data Protection
Tenant-scoped vault storage, configurable production KMS, TLS in transit.
- Network Security
VPC isolation, private endpoints, firewalls, and DDoS protection.
- Threat Detection
Continuous monitoring, anomaly detection, and evidence-backed response.
- Audit & Logging
Immutable audit logs and real-time activity tracking across agents.
- Incident Response
Runbooks, approvals, and policy guardrails for safe remediation.
Our security posture
Proactive. Transparent. Relentless.
Continuous assessments, penetration tests, and a culture of security keep Infravox ahead of threats — with clear status instead of unverified scores.
- Quarterly penetration testing
- Bug bounty program
- Third-party risk assessments
- Continuous compliance monitoring